Insights
Practical writing about the things South African business owners actually ask us. No scare tactics, no jargon, and nothing behind a form. Every article is reviewed by our in house CISSP certified security specialist before it publishes.
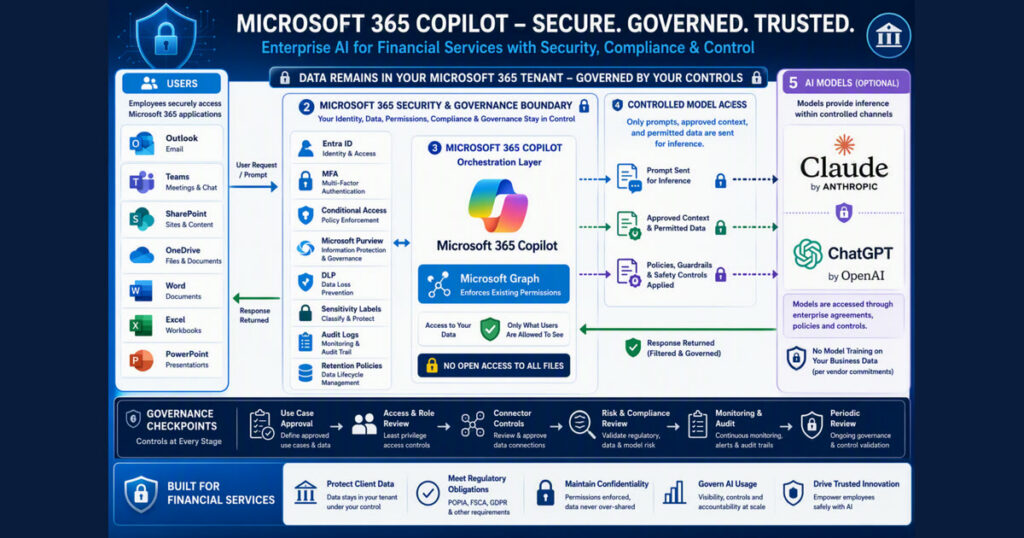
Which AI model should your business choose?
Why the real question is not ChatGPT against Claude against Gemini, but how your business governs and secures AI.
12 October 20265 min read
POPIA for a small business: what Section 19 actually asks for
A plain English walkthrough of the one section of POPIA that governs how you secure personal information, and what it means for a business with no IT department.
18 August 20264 min readRead →POPIA and compliance
What POPIA actually requires from a business with no IT department
POPIA does not ask you to build a security team. It asks for measures that are reasonable for a business your size, and for you to be able to show what they are. Here is what that looks like when nobody in the building is technical.
14 November 20237 min readRead →POPIA and compliance
A POPIA readiness checklist you can work through in an afternoon
Twelve checks, ordered so the ones that change your position most come first. Nothing here is gated and none of it needs a consultant.
12 September 20235 min readRead →POPIA and compliance
Does POPIA apply to CCTV, access control and the visitor book
It does, to all three. Cameras, biometric readers and a clipboard at reception are all collecting personal information, and the clipboard is the one nobody thinks about.
11 July 20235 min readRead →POPIA and compliance
When you have to notify the Information Regulator, and when you do not
Not every security incident is a notifiable breach. Knowing which test applies, and writing down your reasoning either way, is most of the work.
11 April 20236 min readRead →POPIA and compliance
Who has to appoint an Information Officer, and what the job involves
This is the POPIA obligation businesses are most often surprised by, because there is no appointing to be done. If nobody was named, the role already sits with the head of the business.
12 July 20225 min readRead →POPIA and compliance
What to do in the first 24 hours after a data breach in South Africa
The order you do things in changes how bad this gets. If you are in the middle of it now, start at the list and read the reasoning afterwards.
12 April 20226 min readRead →
IT support company in Cape Town: how to judge one from the outside
Every IT company sounds competent on its own website. This is how to assess one when you have no way to check the technical detail yourself, wherever in the country you are.
26 August 20264 min readRead →Managed IT and providers
Managed IT services in South Africa: what the fixed monthly fee should cover
A managed service is not support with a subscription attached. It is a different commercial arrangement, and in South Africa it now carries obligations that the older way of buying IT did not.
25 August 20264 min readRead →Managed IT and providers
Managed IT services in Johannesburg: what to ask before you sign
Every provider in Gauteng will tell you they offer managed IT. The word covers everything from genuine round-the-clock management to reactive support with a monthly invoice attached. These are the questions that tell them apart.
24 August 20265 min readRead →Managed IT and providers
Five questions worth asking your IT provider this week
Fair questions any good provider answers instantly. The answers tell you whether you have a managed service or a repair shop on speed dial.
11 November 20253 min readRead →Managed IT and providers
How to change IT provider without stopping the business
Changing provider is the single biggest reason businesses stay somewhere they have outgrown. It is a project with a known shape, and almost all of the risk sits in one place: whether you hold your own credentials.
10 February 20216 min readRead →Managed IT and providers
What a managed IT service should include, and what to query
Managed is not a protected word. Two quotes using it can describe quite different things, so the useful skill is knowing which questions separate them.
12 May 20206 min readRead →Managed IT and providers
What an SLA should promise, and what it usually does not
Almost every IT agreement contains a response time. Very few contain a resolution time, and the difference between those two words is where the frustration comes from.
11 February 20205 min readRead →Managed IT and providers
How to read an IT quote without an IT background
Two quotes for the same business can look nothing alike and differ by a large multiple. Almost none of that gap is the monthly figure on the front page.
13 February 20185 min readRead →Managed IT and providers
Co-managed IT: when you keep your own person and add a team
One capable person cannot be on holiday, on a project and on the helpdesk at the same time. Co-managed is about the coverage they cannot provide, not about replacing them.
12 July 20175 min readRead →Managed IT and providers
Break-fix or managed: the real cost of paying per incident
Per incident looks cheaper on the invoice, because the invoice only shows the part somebody billed for. The rest of the cost lands on your staff.
15 November 20165 min readRead →
What dark web monitoring actually tells you, and what it does not
It does not scan your systems and it cannot remove anything. Here is what it does do, and why most of what it finds did not leak from you.
12 August 20253 min readRead →Cybersecurity and threats
Why multi-factor authentication is not optional any more
Almost every incident we are called about begins with a working password in somebody else's hands. Multi-factor authentication is what makes a stolen password insufficient on its own.
10 November 20206 min readRead →Cybersecurity and threats
What a phishing simulation tells you that training alone does not
Training produces an attendance register. A simulation produces behaviour, which is a different and less comfortable thing to look at.
18 August 20205 min readRead →Cybersecurity and threats
The signs your email has already been read by somebody else
There is no alert for this. Somebody signing in with a working password looks like you signing in. What gives it away is the housekeeping they do to keep the access.
12 November 20196 min readRead →Cybersecurity and threats
Ransomware in a small South African business: what the week looks like
Not the technical account. What actually happens to a business of forty people, hour by hour and then day by day, and which decisions turn out to matter.
12 February 20196 min readRead →Cybersecurity and threats
Penetration test or vulnerability scan: which one you actually need
One tells you what is exposed. The other tells you what somebody could do with it. Buying the wrong one is how businesses end up with a report nobody acts on.
13 November 20186 min readRead →Cybersecurity and threats
How business email compromise actually works, step by step
There is no malware, nothing to detect and no obvious break-in. Somebody signs in as a member of your staff, reads for a while, and waits for a payment worth redirecting.
14 November 20177 min readRead →Cybersecurity and threats
Why antivirus on the laptop is no longer the whole job
Antivirus is still worth having and it still catches things. The reason it is no longer sufficient is that the attacks that matter most do not involve a file for it to catch.
13 September 20165 min readRead →
Backup is not the same as disaster recovery, and the difference shows up on the worst day
A business can have perfect backups and still be down for two weeks. This is why.
13 May 20253 min readRead →Backup and continuity
What load shedding does to your data, and how to plan for it
The obvious cost is the hours nobody can work. The one that catches businesses out is what an abrupt power cut does to a file that was being written to at the time.
12 November 20245 min readRead →Backup and continuity
Microsoft 365 keeps your mail, not your business. What that means
Microsoft guarantees the service will be there. What is in it is your responsibility, and that distinction is written into the agreement rather than hidden in it.
17 August 20216 min readRead →Backup and continuity
How to test a backup so you know it will actually restore
A backup console showing green tells you a job ran. It does not tell you the data is usable, that anybody knows how to get it back, or how long that would take.
11 May 20215 min readRead →Backup and continuity
RPO and RTO in plain English, and how to set yours
Two numbers, and between them they define what you are actually buying when you buy backup. Most businesses have never been asked for either, which is why the answer usually disappoints on the day.
14 May 20195 min readRead →
IT and POPIA for a law firm: the file is the business
A practice can replace a computer in a morning. It cannot reconstruct a matter, and it cannot un-send a payment that went to the wrong account.
23 September 20265 min readRead →Industry specific
Patient records, POPIA and the practice that runs on one PC
Health information is treated more strictly than ordinary personal information, which raises the standard. Most practices are not far off it, and the gaps are consistent.
23 September 20265 min readRead →Industry specific
The property transfer fraud that starts inside a real email thread
Why estate agencies and conveyancers are targeted, and the one control that stops it.
17 February 20263 min readRead →Industry specific
Why estate agencies get targeted, and what stops it
Property transactions combine large amounts, known timelines and parties who have never done this before. That combination is why agencies are chosen rather than stumbled upon.
14 February 20235 min readRead →Industry specific
Sage on a network that was never designed for it
Slow month end, records that will not release, and a data file sitting on the accountant's desktop. Almost none of this is Sage misbehaving. It is the network and the storage underneath it.
13 August 20196 min readRead →Industry specific
Downtime on the factory floor is not an IT problem until it is
A plant runs on machines whose control software was frozen the day they were commissioned. The question is not how to update them. It is what they are allowed to reach.
10 July 20185 min readRead →
Where your data lives when you move to the cloud, and why it matters
POPIA restricts sending personal information outside South Africa unless certain conditions are met. That does not rule out international cloud services, and it does mean somebody should have thought about it.
23 September 20265 min readRead →Cloud and Microsoft 365
Teams Phone instead of a PABX: what changes on day one
The calls themselves are the easy part. What takes the thinking is reception, the things plugged into the old system, and what happens when the line drops.
18 February 20256 min readRead →Cloud and Microsoft 365
What Microsoft 365 licence do you actually need
The gap between the cheap end and the expensive end is mostly security and device management. Which means the right question is not which licence, it is which capabilities you need.
9 February 20225 min readRead →Cloud and Microsoft 365
Moving to Microsoft 365 without losing a day of work
The mail is the part everybody plans for. The delays come from the shared drive nobody had mapped and the scanner that emails to an address on the old server.
16 November 20215 min readRead →
IT support in Sandton when your team is split across provinces
Two offices in different provinces is not two IT setups. It is one, with a question about which parts have to be local and which should not be.
23 September 20265 min readRead →Local
What Ballito businesses ask us most about connectivity
The questions are consistent and the answers are mostly about contracts rather than technology. Almost none of them are about speed.
14 May 20245 min readRead →Local
Choosing IT support on the KZN North Coast
Local means something specific here, and it is not only distance. It is whether somebody can be at your premises this afternoon, and whether they answer in the third week of December.
14 February 20175 min readRead →Four more are written and in review: what legal practices and healthcare practices each need to ask about their own regulator, where Microsoft 365 data actually lives, and how a team split between the North Coast and Sandton gets supported. Nothing goes up until it has been checked, and nothing goes behind a form. If there is something you want answered, ask us and we will write it.
An IT audit,
and a free dark web scan.
Our specialists audit your network, computer systems, Microsoft 365 environment, cybersecurity controls and backups on site, then hand you a written report with a prioritised action plan. Every audit includes a free dark web exposure scan, run against your domain before anybody visits.
Worried about what it takes to move?
Changing IT provider is the single biggest reason businesses stay somewhere they have outgrown. We plan the move around your working week, and we help carry the cost of getting across. Ask us how that works when we speak.